Part 2 of 5 in the Flipper Zero series. Part 1: what it actually is and what it can’t do.
Most buildings I have walked into run on one of four card technologies, and the reception desk usually cannot tell you which. That matters, because the four have wildly different security properties and they look identical in a wallet. This part is about the two badge radios on the Flipper Zero, 125 kHz and 13.56 MHz, and what they reveal when you point them at your own cards.
Same rules as part 1: hardware I own, cards I own, and a defender’s goal. A work badge usually belongs to your employer, so treat it as someone else’s card and get written permission before testing it. If you are auditing a site, get written permission first.
Two radios, four families
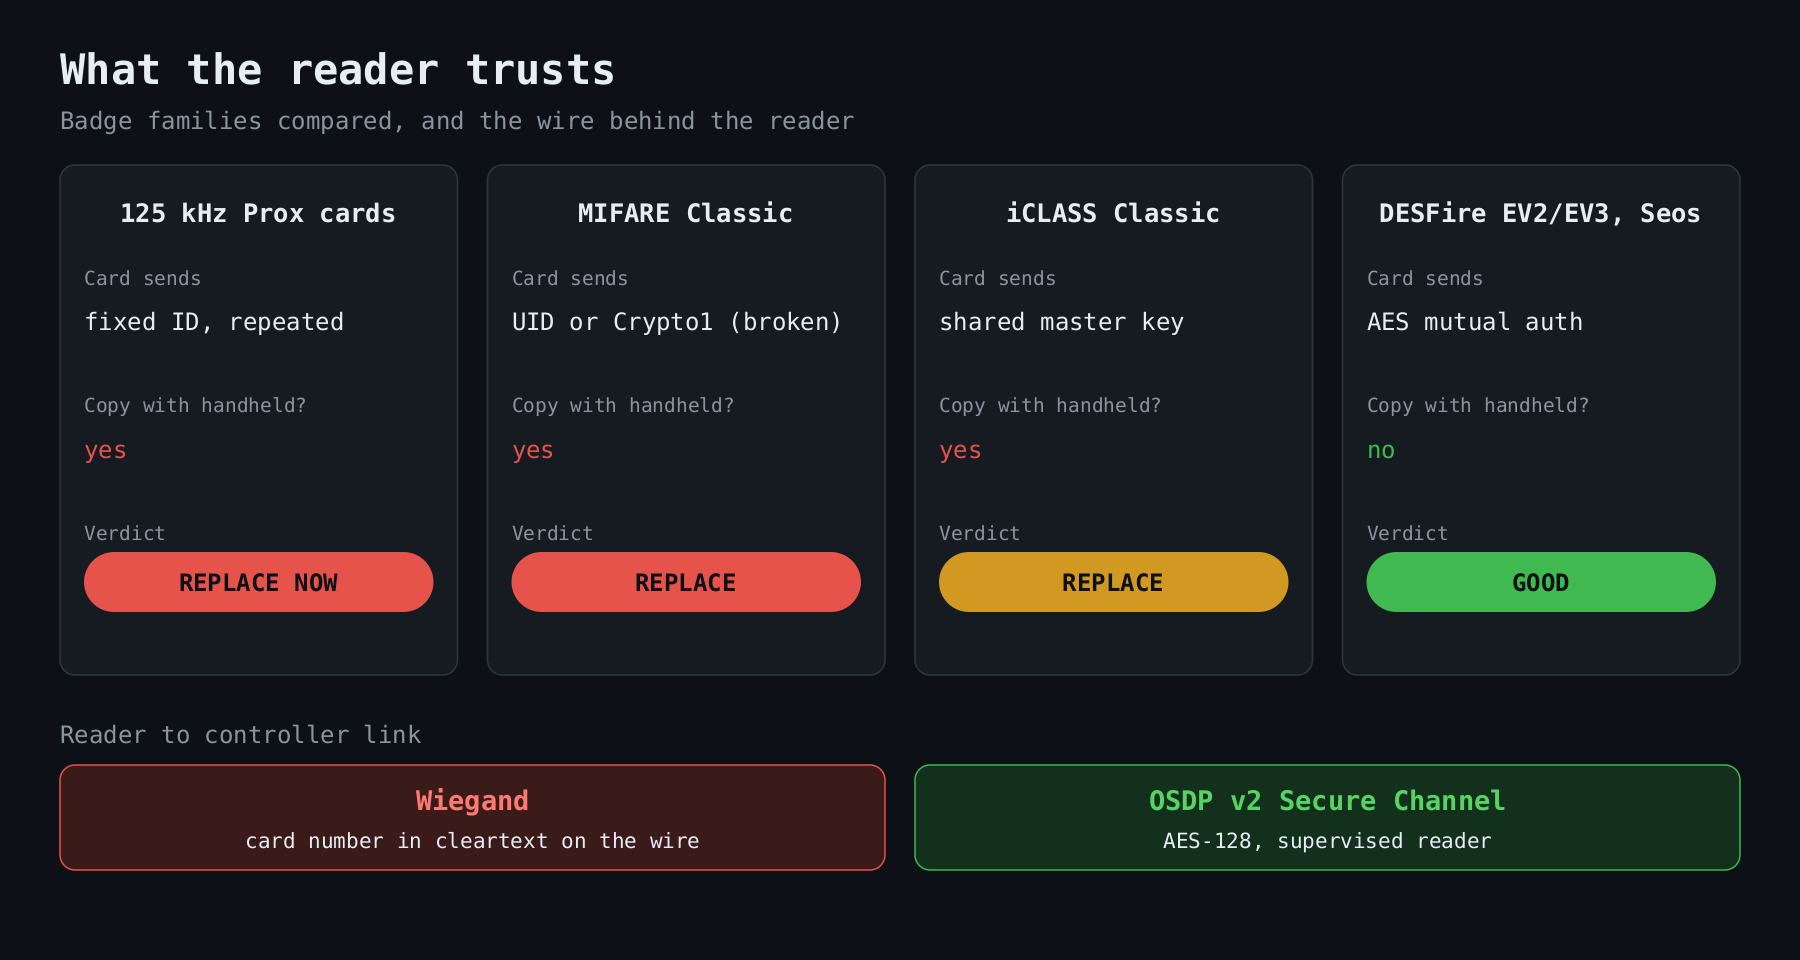
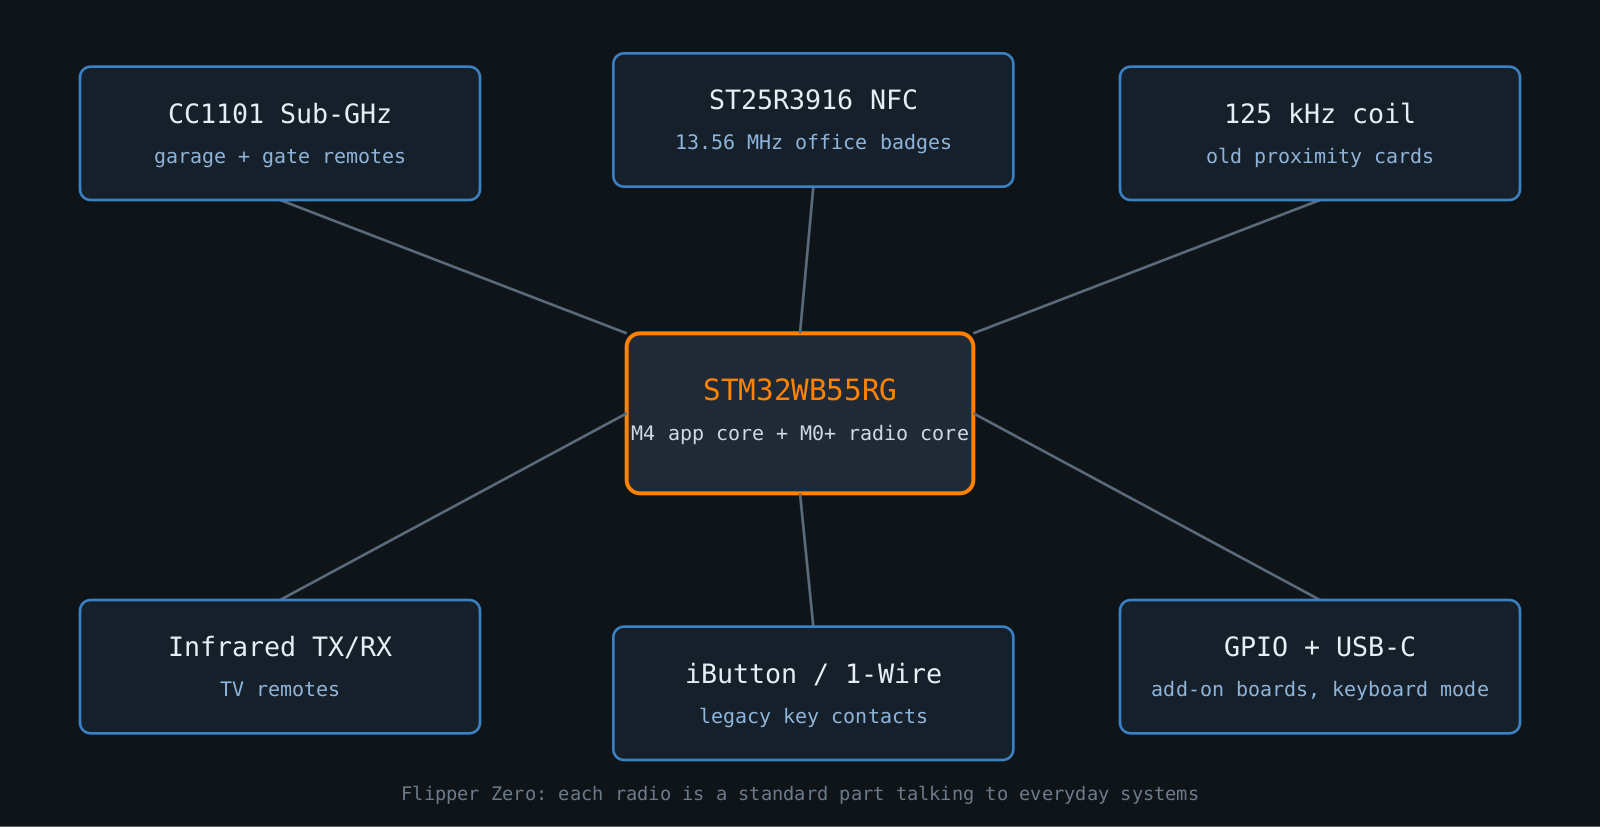
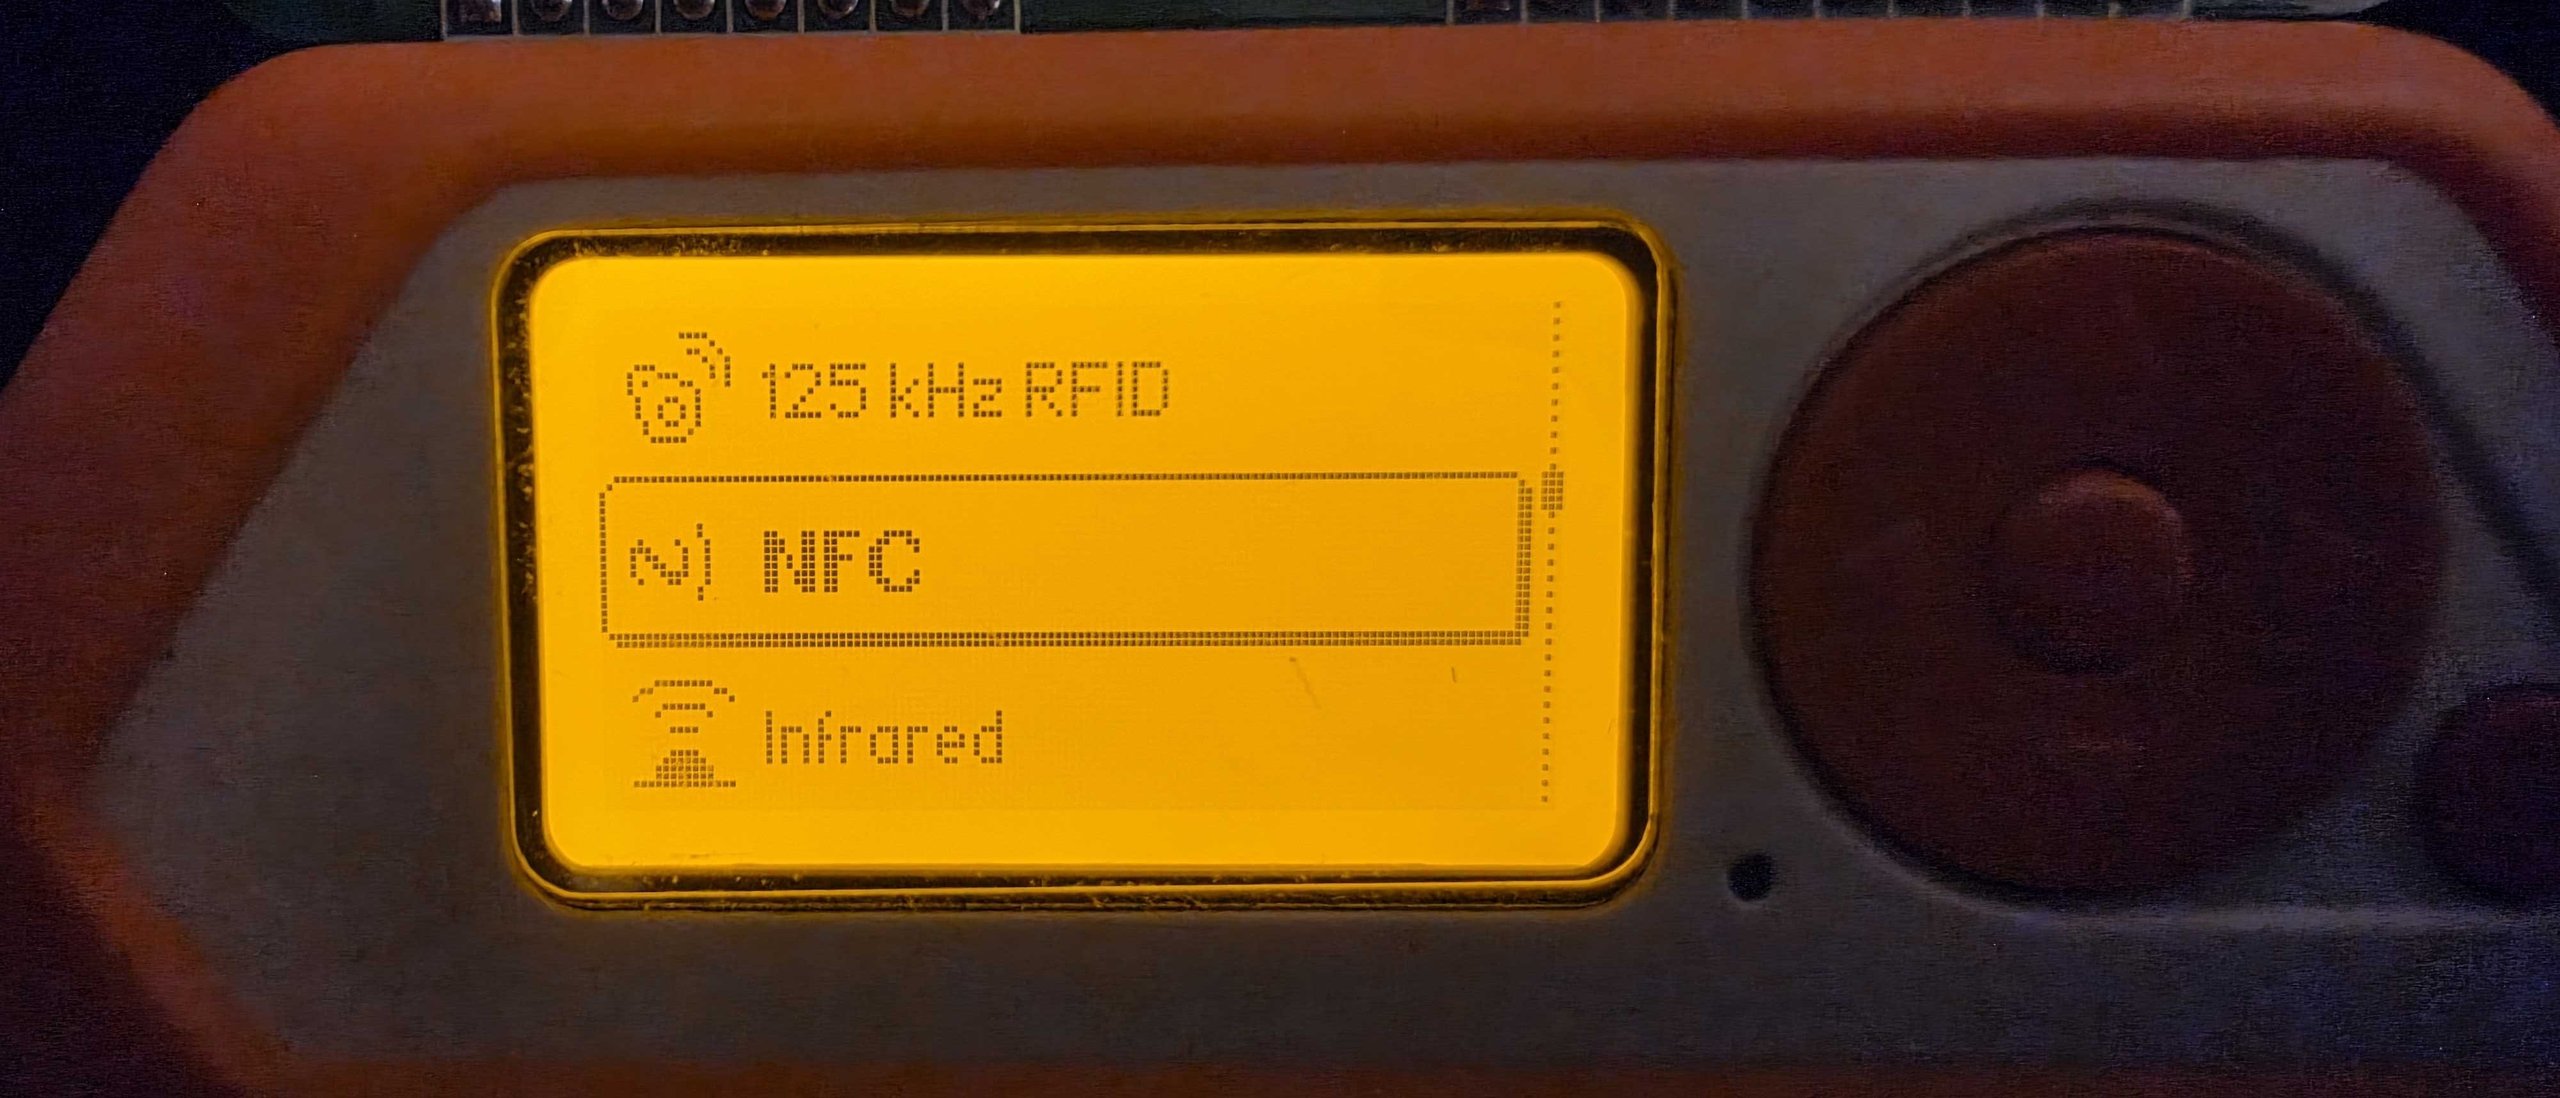
The low frequency radio at 125 kHz reads old proximity cards. EM4100 and HID Prox are the common ones. The high frequency radio at 13.56 MHz covers ISO 14443 and the NFC family: MIFARE Classic, MIFARE Ultralight, DESFire and the rest. HID’s iCLASS also lives at 13.56 MHz, but it is based on ISO 15693 and Flipper handles it separately in its Picopass app. The Flipper’s main menu sorts the cards under “125 kHz RFID” and “NFC”, and its read screen tells you which family it found for most of them. That screen is the first step of the audit, not the whole of it.
125 kHz: an ID, not a credential
An EM4100 tag transmits a 40 bit value, over and over, to anything that powers it up. There is no key, no challenge and no secret. HID Prox is much the same idea wrapped in the 26 bit Wiegand format called H10301: one parity bit, an 8 bit facility code, a 16 bit card number and a closing parity bit.
You can decode that yourself in a few lines:
def parse_h10301(bits: str):
    assert len(bits) == 26
    facility = int(bits[1:9], 2)
    card = int(bits[9:25], 2)
    return facility, card

print(parse_h10301("00000001100000000000011111"))  # (3, 15)
Sixteen bits of card number means 65,536 possible values per facility code, and facility codes are 8 bits. Nothing in the card proves it is the original. Copying one to a blank tag takes seconds with a Flipper or a ten dollar reader. I have never seen a reason to defend this technology beyond “we have not got round to replacing it”.
MIFARE Classic: encryption that did not hold
MIFARE Classic is the long-lived 13.56 MHz card from NXP, and it shipped with a proprietary cipher called Crypto1 and 48 bit keys. In 2008 researchers at Radboud University Nijmegen (Garcia and colleagues) published “Dismantling MIFARE Classic” at ESORICS, after Karsten Nohl and Henryk Plötz had reverse engineered the cipher from the chip. In 2009 a nested attack from the same group (IEEE S&P) recovered every key on a card given one known key, and Courtois published a variant that needed none. In 2015 Meijer and Verdult’s “hardnested” attack handled the hardened cards that NXP issued after the first breaks.
In practice the weak point is often not the cipher at all. Many deployments leave sectors on the factory default key, FFFFFFFFFFFF, and many readers only look at the 4 or 7 byte UID. A UID is not a secret, and there are “magic” cards sold with a rewritable UID block. If your reader just checks the UID, the cryptography is irrelevant.
You can see what you have without special tools. With libnfc and an ordinary USB reader:
$ nfc-list
ISO/IEC 14443A (106 kbps) target:
    ATQA (SENS_RES): 00  04
       UID (NFCID1): 04  a2  3b  1c
      SAK (SEL_RES): 08
Those values are illustrative, not from a real card, but the SAK byte is real: 0x08 identifies a MIFARE Classic 1K, 0x18 a 4K. A DESFire card answers differently, with a SAK of 0x20 and ISO 14443-4 support. The Flipper shows the same information on its screen without any laptop.
iCLASS: the shared key problem
HID’s original iCLASS (now called iCLASS Classic) used a master key shared across the product line. Milosch Meriac extracted it in 2010, and the 2012 paper “Dismantling iClass and iClass Elite” went on to break the Elite key diversification as well. Once a master key is public, every site using the default configuration is exposed, whether it knows or not. HID’s replacements, iCLASS SE and the Seos credential, moved to modern cryptography.
What good looks like
The fix is a card that authenticates with a per-card key, using a standard algorithm, and a reader that actually checks. MIFARE DESFire EV2 and EV3 use AES with mutual authentication, and Seos does too. Whichever you choose, ask your vendor four questions:
1. Does the card use AES, and are keys diversified per card?
2. Does the reader verify the credential, or only read a UID?
3. Is the reader-to-controller link OSDP with Secure Channel enabled and a unique key, not Wiegand or the default install key?
4. Who holds the master keys, and where do they live?
The third question is the one people forget. Wiegand sends the card number down a few wires in cleartext, so a tap on the cable behind the reader defeats the best card on the market. OSDP v2 adds an AES-128 secure channel and also lets you supervise the reader, so a pulled or replaced one raises an alarm. I would put reader wiring on the same priority list as the cards.
One caveat, since I like to be straight about limits: even a strong card can be relayed. An attacker who stands near the victim and near the door can pass the radio exchange along in real time, and the crypto will happily succeed. Distance bounding is the research answer. Some cards, DESFire EV2 and EV3 among them, offer a proximity check feature, but I rarely see it switched on. Defend with a second factor at sensitive doors, or camera coverage, rather than assuming the card solves it.
Migrating without a big bang
Nobody swaps every card in a weekend. Dual technology readers that accept the old and new credential let you issue new cards gradually, with a cutoff date after which the legacy mode is disabled in the controller. Skipping that last step is the usual failure, so put it in the project plan with a name next to it. I have seen buildings run “temporary” legacy support for six years.
Start with the audit. Tap your own badge on a reader that tells you what it is, write down the family, and compare it with the list above. If the answer is 125 kHz or MIFARE Classic, you have your project.
Part 3 moves to Sub-GHz remotes, rolling codes and how gates should be built.
Other parts of the Flipper Zero series: part 1, part 2, part 3, part 4, part 5.