Skip to content

CanuteTheGreat's BLOG

    • About
    • I Love Coffee!
  • Hardware hacking, part 5: reading SPI flash without wrecking it or fooling yourself

    Hardware hacking, part 5: reading SPI flash without wrecking it or fooling yourself

    Hardware, Security
  • Hardware hacking, part 2: the bench I work on and what each tool is for

    Hardware hacking, part 2: the bench I work on and what each tool is for

    Hardware, Security
  • Hardware hacking, part 4: finding the UART console on a router I own

    Hardware hacking, part 4: finding the UART console on a router I own

    Hardware, Security

    Part 4 of 7 in the Hardware hacking series. Part 1: updating the firmware on a Pinecil V2. Part 2: the bench I work on. Part 3: using my 5V FTDI cable on 3.3V UARTs. The first thing I check on a router I own is whether it has a serial console, and whether that…
  • Hardware hacking, part 3: using my 5V FTDI cable on 3.3V UARTs without killing the board

    Hardware hacking, part 3: using my 5V FTDI cable on 3.3V UARTs without killing the board

    Hardware, Security
  • Horcrux dev log: breaking my own HA cluster on three old laptops

    Horcrux dev log: breaking my own HA cluster on three old laptops

    Linux, Software Engineering
  • Designing an Incident Response Runbook That Actually Gets Used Under Pressure

    Designing an Incident Response Runbook That Actually Gets Used Under Pressure

    Security
  • Horcrux dev log 6: clustering, an ISO you can install from, and real laptops

    Horcrux dev log 6: clustering, an ISO you can install from, and real laptops

    Linux, Software Engineering
  • Patronus dev log 5: security holes, netlab, and the 0.2.0 release

    Patronus dev log 5: security holes, netlab, and the 0.2.0 release

    Security, Software Engineering
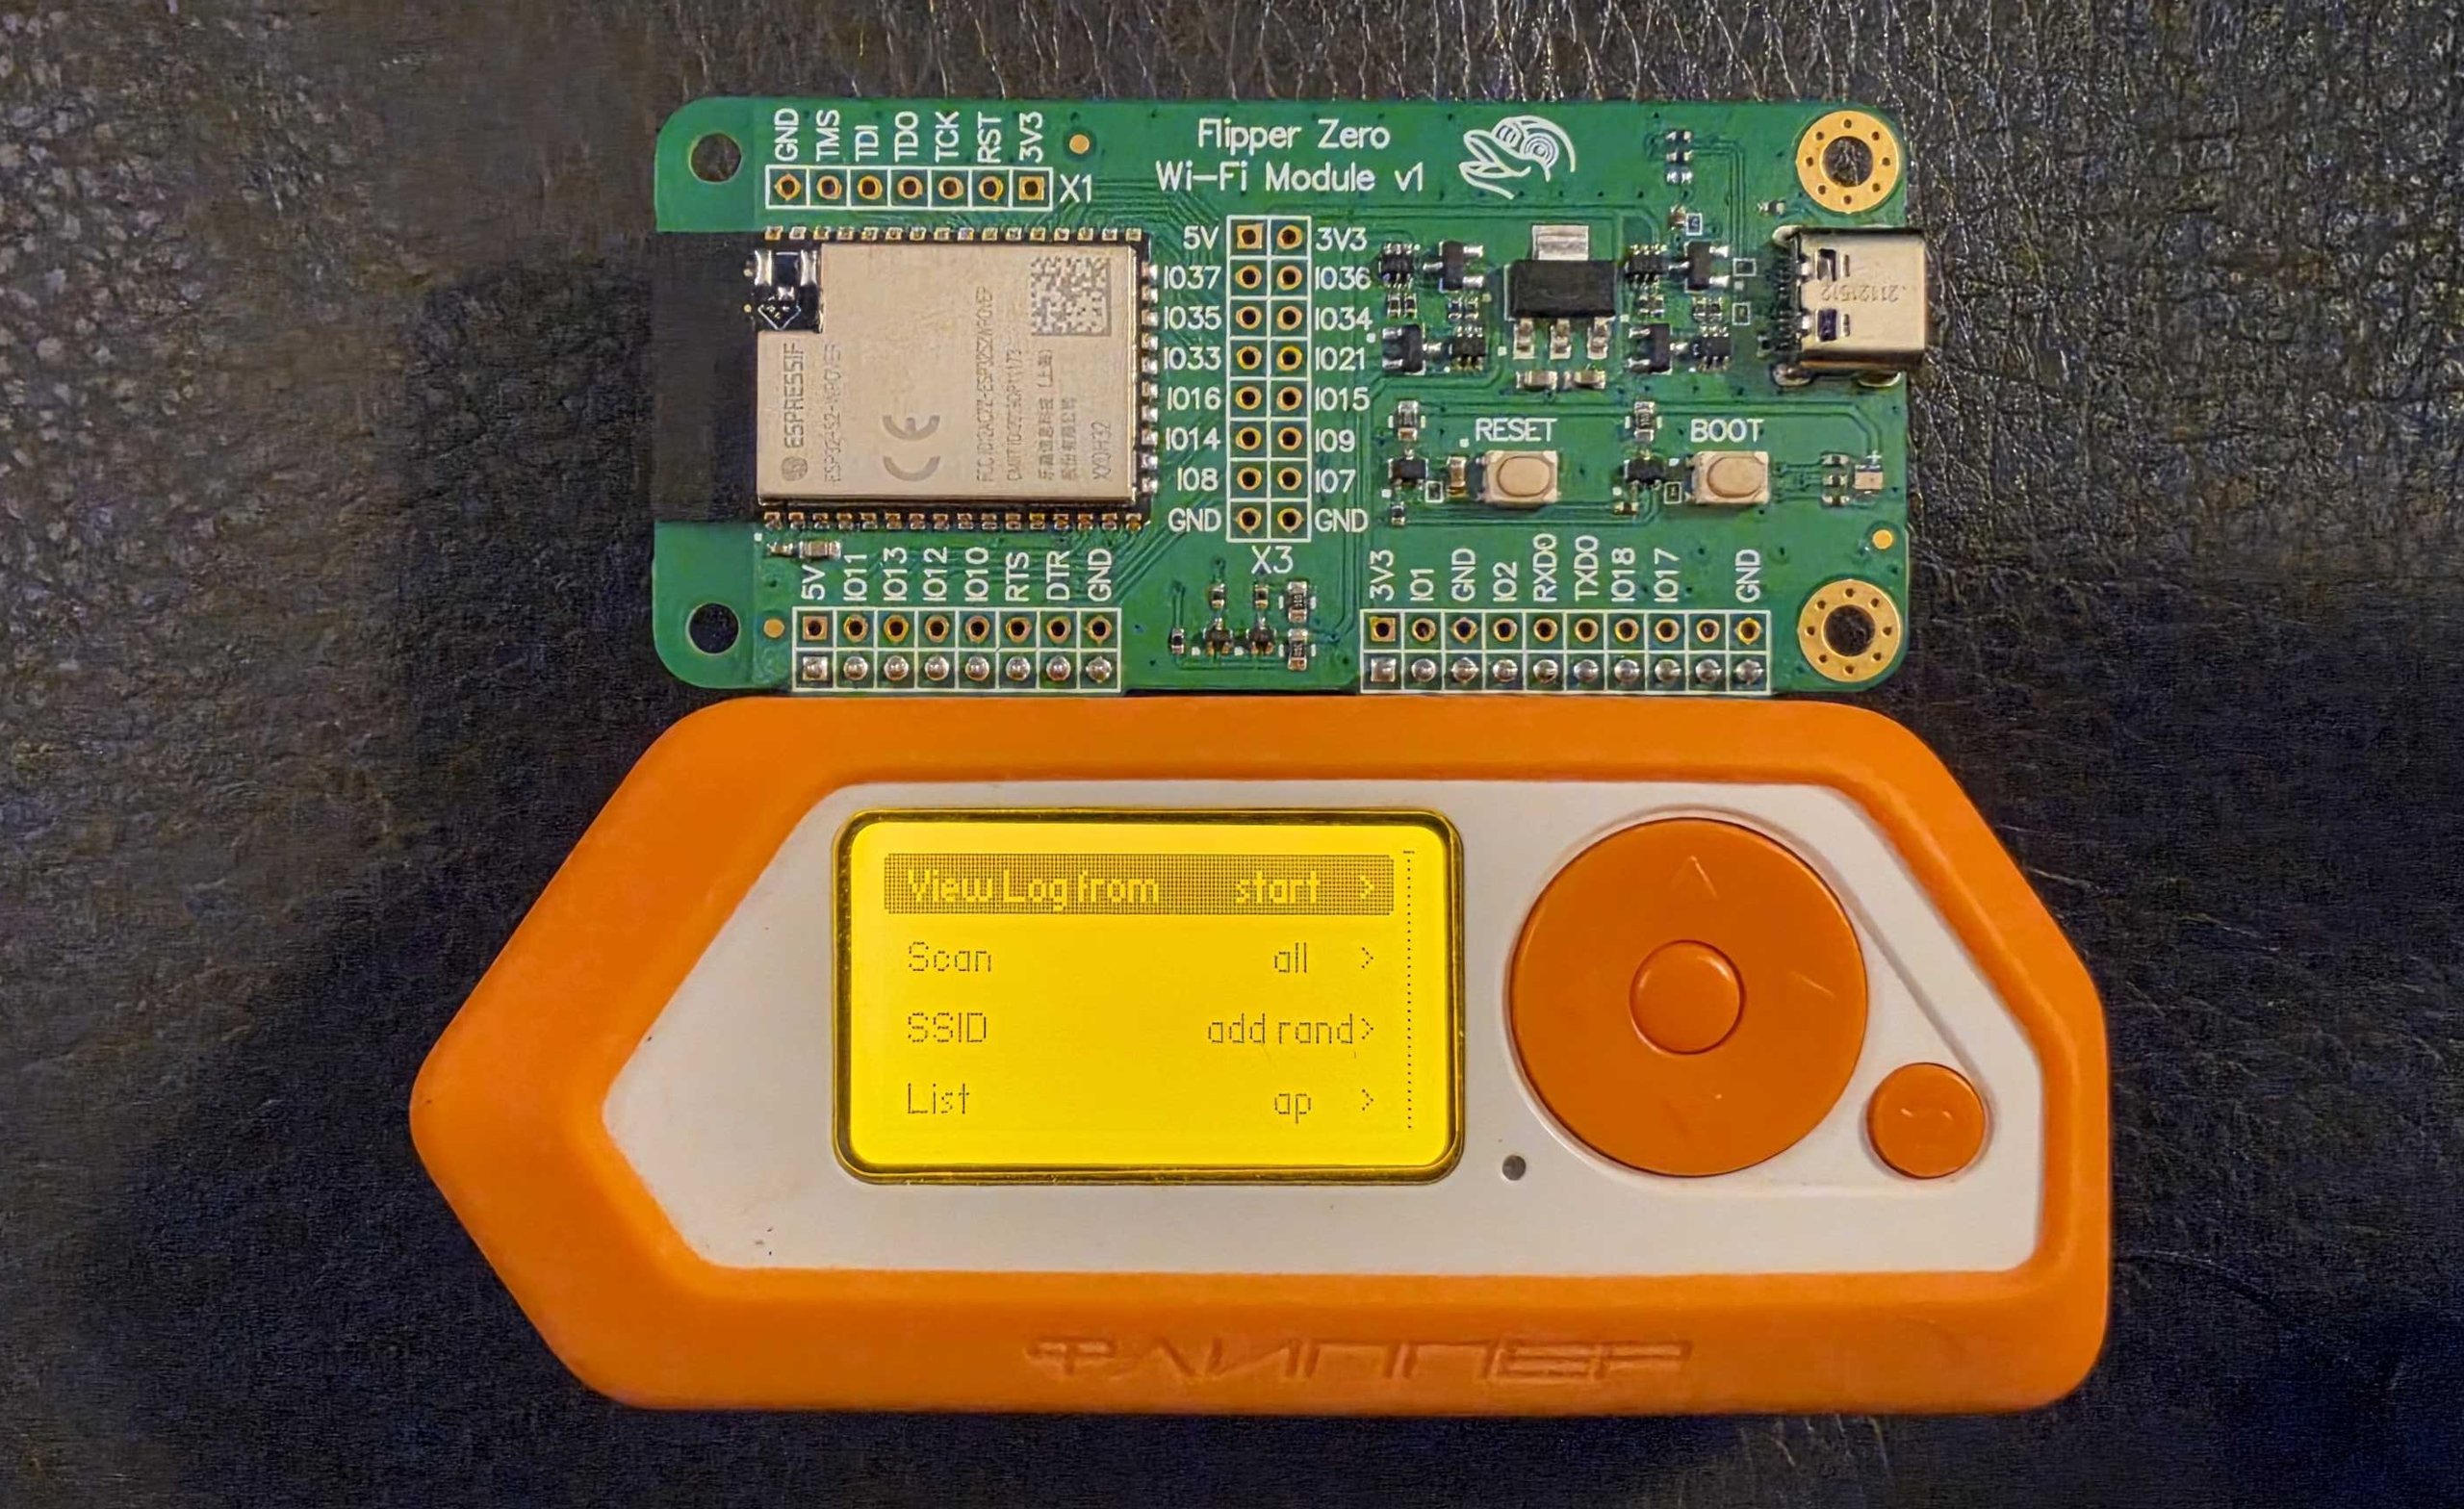
  • Flipper Zero, part 5: the Wi-Fi board, rogue access points and why 802.11w matters

    Flipper Zero, part 5: the Wi-Fi board, rogue access points and why 802.11w matters

    Security, Technology
  • Flipper Zero, part 4: USB keystroke injection and how to lock USB down

    Flipper Zero, part 4: USB keystroke injection and how to lock USB down

    Security, Technology
  • Flipper Zero, part 3: Sub-GHz remotes, rolling codes and how gates should be built

    Flipper Zero, part 3: Sub-GHz remotes, rolling codes and how gates should be built

    Security, Technology
  • Hardware hacking, part 1: updating the firmware on a Pinecil V2

    Hardware hacking, part 1: updating the firmware on a Pinecil V2

    Hardware, Security
  • Flipper Zero, part 2: why so many office badges are weaker than they look

    Flipper Zero, part 2: why so many office badges are weaker than they look

    Security, Technology
1 2 3 … 17
Next Page

CanuteTheGreat's BLOG

My random musings.

Designed with WordPress